- Platforms
- iOSAndroid
- Products
- IntuneOutlookExchange OnlinePKI
- Result
- Users sign and encrypt email in Outlook for iOS and Android without installing certificates by hand
Overview
Deliver S/MIME signing and encryption certificates to Outlook on iPhone and Android automatically: SCEP for signing, imported PFX for encryption, and Exchange Online to validate them.
Outlook for iOS and Android can read and send signed and encrypted email with S/MIME (Secure/Multipurpose Internet Mail Extensions), and install encryption certificates from senders.
S/MIME certificates reach mobile devices manually or automatically. With automated delivery, signing certificates usually come from SCEP and are unique per device and user.
Encryption certificates are unique per user and shared across that user's devices. An administrator imports them into Microsoft Intune from the certificate authority (CA) on behalf of the user (see PKCS imported certificates).
This post covers automated S/MIME certificate delivery for signing (SCEP) and encryption (PKCS imported certificate).
To protect Outlook and other mobile apps, see also my post on app protection policies (Data Protection Framework).
Prerequisites
Before you start, check that you have the following.
| Area | What you need | Docs |
|---|---|---|
| Licence | Microsoft Intune Plan 1 and Exchange Online for the users | Licensing |
| Admin role | Application Manager and Policy and Profile Manager in Intune; Exchange administrator for Set-SmimeConfig | Roles |
| PKI | An enterprise CA with the CRL published to the internet | S/MIME prerequisites |
| Certificate Connector for Microsoft Intune, for SCEP signing and imported PFX encryption certificates | ConnectorSCEPImported PFX | |
| Exchange Online | A virtual certificate collection (.sst) with your root and intermediate CAs | Configure S/MIME |
| Devices | iOS/iPadOS or Android Enterprise devices enrolled in Intune, with Outlook and Company Portal | Automated delivery |
Which certificate type can do what (see certificates in Intune):
| Type | Authentication | S/MIME signing | S/MIME encryption |
|---|---|---|---|
| PKCS imported certificate | Yes | Yes | |
| PKCS#12 (PFX) | Yes | Yes | |
| SCEP | Yes | Yes |
Configuration
Set up the Outlook policy, import the certificates, then let Exchange Online validate them.
App configuration policy for Outlook S/MIME
In the Intune admin center (intune.microsoft.com), go to Apps > Configuration > Create > Managed devices and configure the Outlook S/MIME settings:
- Enable S/MIME: Yes
- Allow user to change setting: Yes
- Deploy S/MIME certificates from Intune: Yes
- Signing certificates: SCEP (or PKCS imported certificates)
- Encryption certificates: PKCS imported certificates
- End-user notifications: Company Portal
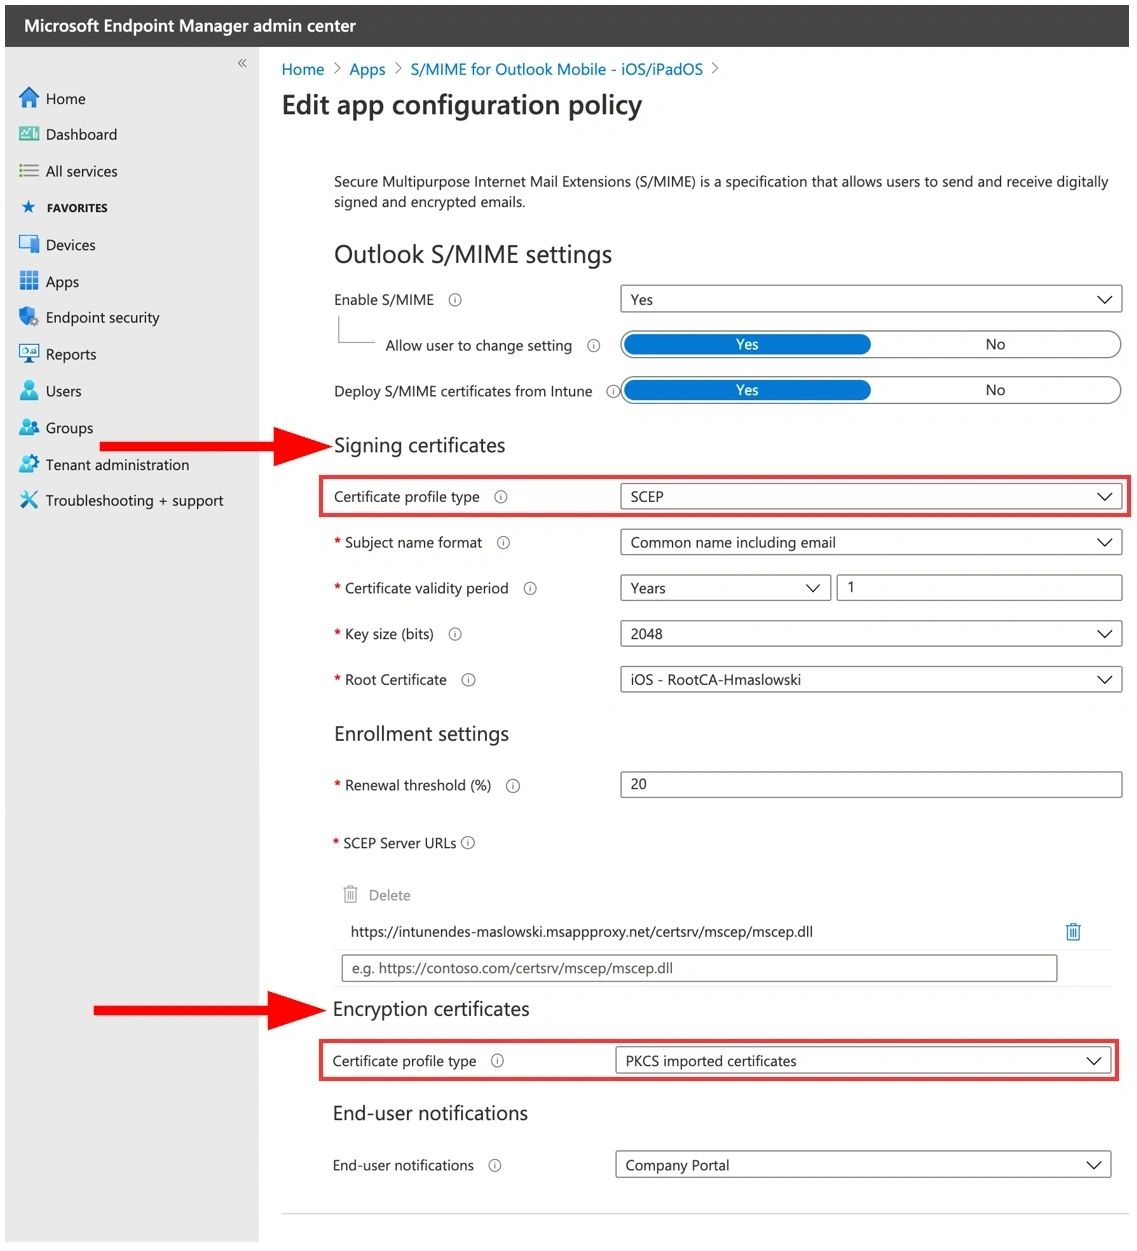
Assign the policy to the users or devices that have Outlook installed.
Update (October 2026): the policy also offers derived credentials as a certificate source, and settings to encrypt or sign all emails and an LDAP URL for certificate lookup. For Android, create the policy for Android Enterprise, all profile types (see automated certificate delivery).
Note: automated delivery works only on devices managed by Intune. Third-party MDM is not supported.
Import and deploy the PFX encryption certificate
An administrator does these steps on behalf of the user (see Import PFX certificates to Intune). The PowerShell module comes from the PFXImportPowershell project on GitHub, which you build with Visual Studio.
My commands to import the PKCS/PFX certificate (hubertm.pfx) for the user hubertm@hmaslowski.com:
Import-Module .\IntunePfxImport.psd1
Set-IntuneAuthenticationToken -AdminUserName "hubertm@hmaslowski.com"
$SecureFilePassword = ConvertTo-SecureString -String "<password>" -AsPlainText -Force
$userPFXObject = New-IntuneUserPfxCertificate -PathToPfxFile "C:\hubertm.pfx" $SecureFilePassword "hubertm@hmaslowski.com" "Microsoft Software Key Storage Provider" "PFXEncryptionKey" "smimeEncryption"
Import-IntuneUserPfxCertificate -CertificateList $userPFXObject
To check that the encryption certificate (smimeEncryption) was imported, run:
Get-IntuneUserPfxCertificate -UserList "hubertm@hmaslowski.com"Id : <id>
Thumbprint : <thumbprint>
IntendedPurpose : SmimeEncryption
UserPrincipalName : hubertm@hmaslowski.com
StartDateTime : 23/10/2020 08:21:26 +00:00
ExpirationDateTime : 23/10/2021 08:21:26 +00:00
ProviderName : Microsoft Software Key Storage Provider
KeyName : PFXEncryptionKey
PaddingScheme : OaepSha512If you don't use SCEP for signing, you can import a second PFX for signing (smimeSigning) in the same way:
$userPFXObject = New-IntuneUserPfxCertificate -PathToPfxFile "C:\signing.pfx" $SecureFilePassword "hubertm@hmaslowski.com" "Microsoft Software Key Storage Provider" "PFXEncryptionKey" "smimeSigning"
Import-IntuneUserPfxCertificate -CertificateList $userPFXObject
The user now has both certificates in Intune:
Id                   : <id>
Thumbprint           : <thumbprint>
IntendedPurpose      : SmimeSigning
...

Id                   : <id>
Thumbprint           : <thumbprint>
IntendedPurpose      : SmimeEncryption
...
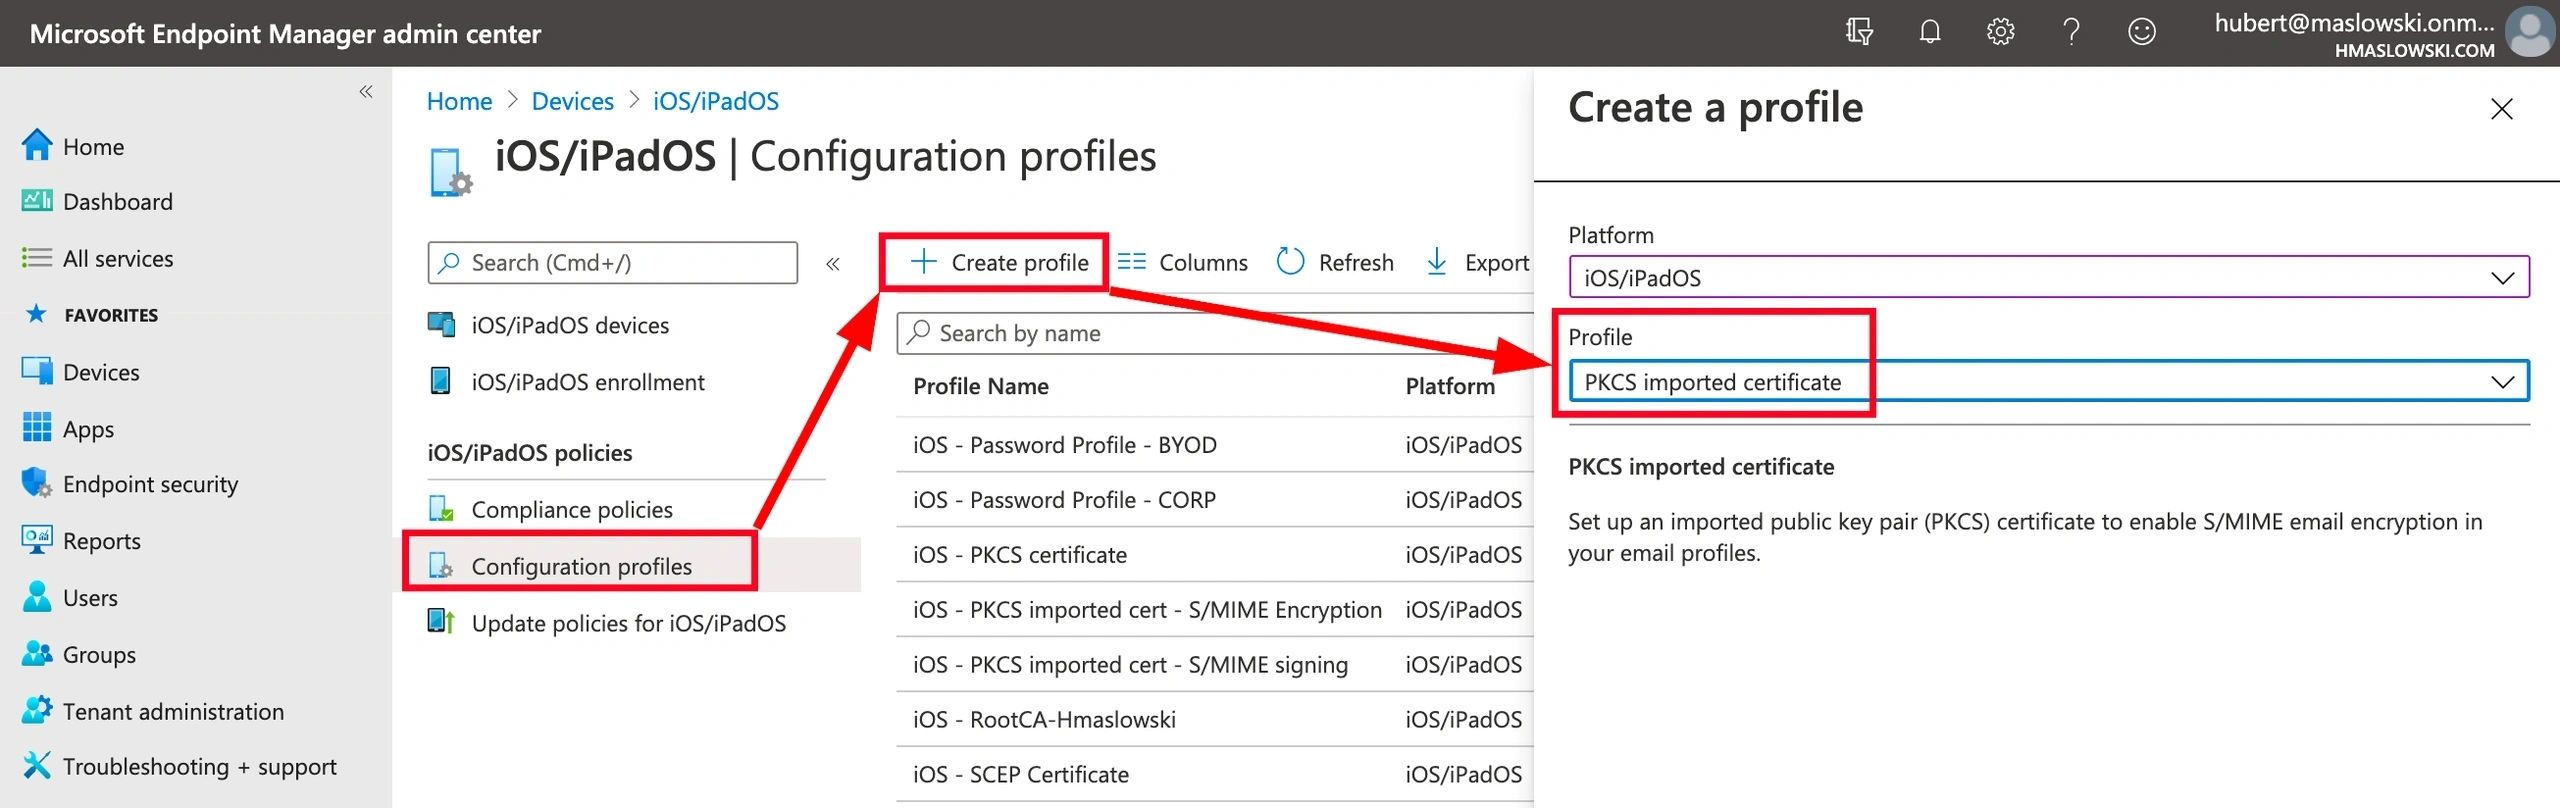
Deliver the imported certificates with a PKCS imported certificate profile under Devices > iOS/iPadOS > Configuration > Create, one profile per platform and purpose:

Set up Exchange Online
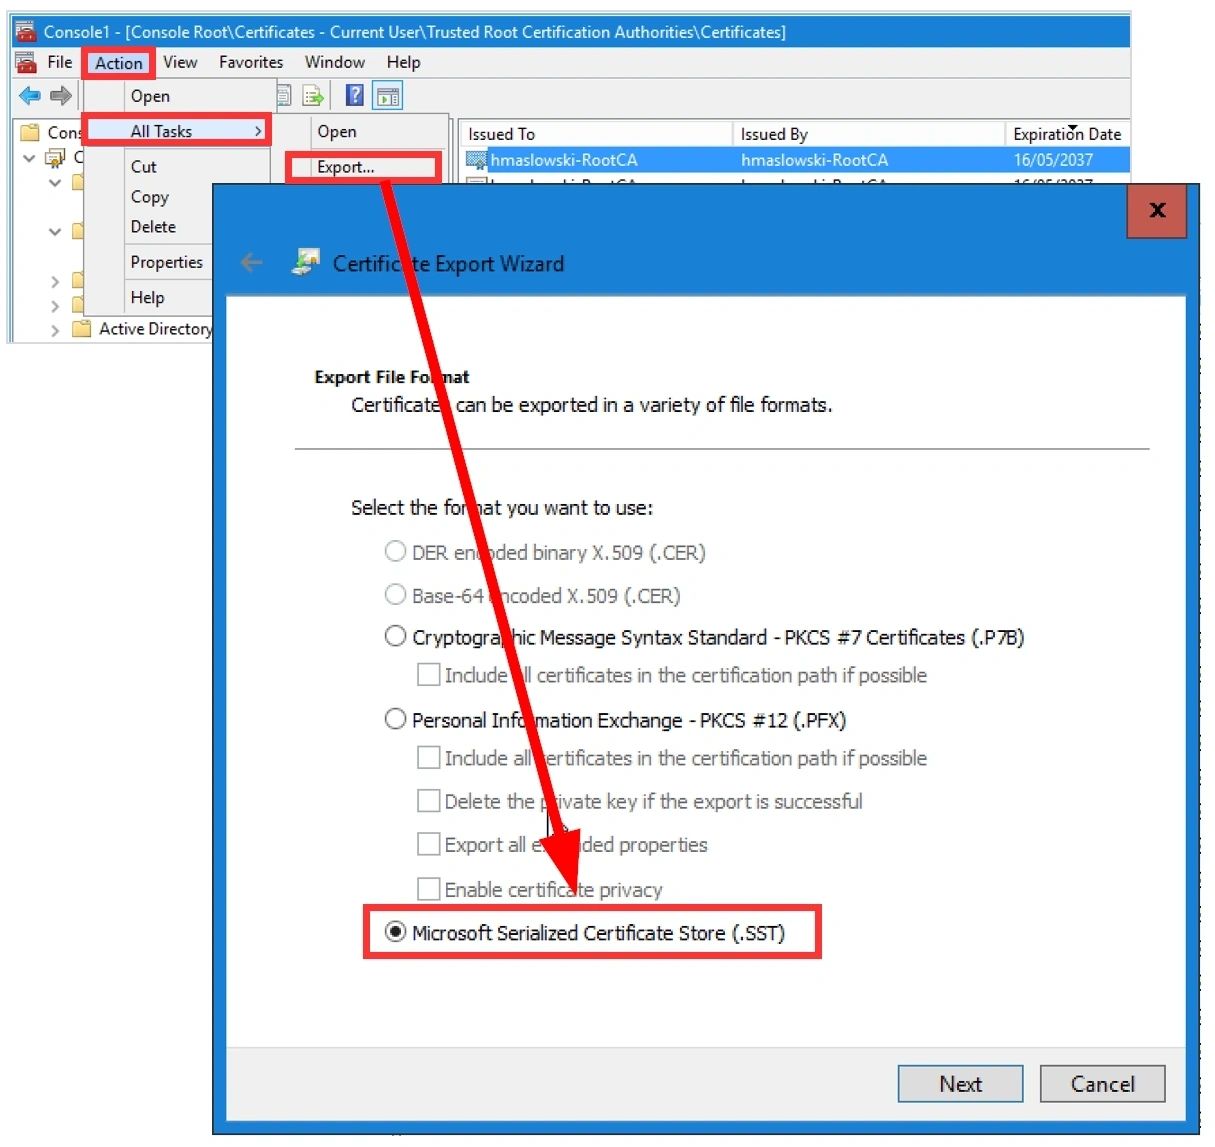
Exchange Online validates S/MIME certificates against a virtual certificate collection, a certificate store file with the .sst extension that holds your root and intermediate CA certificates (see Configure S/MIME in Exchange Online).
Export the CA certificates to an .sst file in the Certificates MMC with Action > All Tasks > Export:
Or export them with PowerShell:
Get-ChildItem -Path Cert:\LocalMachine\My
$cert = Get-ChildItem -Path Cert:\LocalMachine\My\<Thumbprint>
Export-Certificate -Cert $cert -FilePath C:\rootca.sst -Type SST
Then import the .sst file with Exchange Online PowerShell:
Set-SmimeConfig -SMIMECertificateIssuingCA ([System.IO.File]::ReadAllBytes('C:\rootca.sst'))The 2020 version used Get-Content -Encoding Byte, which doesn't work in PowerShell 7. Check the result with Get-SmimeConfig:
Get-SmimeConfig...
SMIMECertificateIssuingCA : {0, 0, 0, 0...}
SMIMECertificatesExpiryDate : 16/05/2037 14:00:56
SMIMEExpiredCertificateThumbprint : <thumbprint>
...User Experience
Company Portal installs the certificates, then Outlook can sign and encrypt.
On my iPhone (iOS 14), the Company Portal app delivers the S/MIME certificates and the user gets a notification to install them:

Finishing the installation in Company Portal:

In Outlook for iOS, compose a new message and turn on Sign and/or Encrypt:

A signed and an encrypted email:
