- Platforms
- iOSiPadOS
- Products
- IntuneApple BusinessEntra ID
- Result
- A new or existing iPhone enrolls in Intune during Setup Assistant, supervised, with its VPP apps installed silently
Overview
Connect Apple Business to Microsoft Intune, create the ADE enrollment policy, sync VPP apps, and enroll a supervised iPhone that installs its apps silently.
In an earlier post I described User Enrollment for personal (BYOD) iPhones and iPads, with Managed Apple Accounts (formerly Managed Apple IDs) provisioned through federation with Microsoft Entra ID (formerly Azure AD). You can read it here.
This time I look at Automated Device Enrollment (ADE, formerly DEP). It lets organizations configure and manage company-owned iPhones and iPads (and Macs and Apple TVs) without touching the devices. I have a separate post on Macs.
Devices enrolled with ADE become supervised automatically (iOS 13 and iPadOS 13.1 and later). Supervision unlocks extra management features: silent app installation, app restrictions, locked enrollment, kiosk (single app) mode, Activation Lock bypass and more. Supervision has been around since iOS 5 (October 2011), but since iOS and iPadOS 13 it is always on for devices enrolled with ADE.
Apple Business (formerly Apple Business Manager) is a free web portal (business.apple.com) for deploying company devices, like Samsung Knox Mobile Enrollment and Google zero-touch enrollment for Android. ADE needs it. Apple Business works with most MDM platforms (Microsoft Intune, Omnissa Workspace ONE UEM, Citrix Endpoint Management and others), which it calls external device management services. It is also where you buy apps and books in volume (Apps and Books, formerly the Volume Purchase Program, VPP).
Note: Apple Business Manager replaced the standalone DEP and VPP portals, which closed on December 1, 2020.
In this post I connect Apple Business to Intune, enroll new or existing iPhones and iPads with ADE, and install public apps silently in volume (Company Portal for the first setup, then Microsoft Edge and the Microsoft 365 apps).
Prerequisites
Before you start, check that you have the following.
| Area | What you need | Docs |
|---|---|---|
| Licence | Microsoft Intune Plan 1 for each user (device-only licences for userless devices) | Licensing |
| Microsoft Entra ID P1 for dynamic groups | Dynamic groups | |
| Admin role | Policy and Profile Manager in Intune for ADE tokens, enrollment policies and sync | Roles |
| Administrator or Device Manager in Apple Business, to connect the MDM service and download tokens | Apple Business | |
| Intune | MDM authority set to Intune and a valid Apple MDM push certificate (renewed every year) | Push certificate |
| Apple Business | An Apple Business account; verify the organization within 60 days with a D-U-N-S Number, EIN, DNS record or App Store Connect | Sign up |
| Devices from an Apple reseller or carrier, or added with Apple Configurator (iOS 16 and later) | SuppliersApple Configurator | |
| Devices | iPhones and iPads with iOS/iPadOS 18 or later; supervised automatically with ADE on iOS 13 and iPadOS 13.1 and later | Supported platformsSupervision |
Configuration
Connect Apple Business first, then create the enrollment policy, groups and apps.
| Step | Console | What you set |
|---|---|---|
| 3.1 | Intune | ADE token from Apple Business |
| 3.2 | Intune | iOS/iPadOS enrollment policy |
| 3.3 | Entra | Dynamic device groups for iPhone and iPad |
| 3.4 | Intune | Apps and Books content token |
| 3.5 | Apple Business | Devices from a reseller or Apple Configurator |
Connect Intune to Apple Business for ADE
Intune admin center
With the Apple MDM push certificate in place, create an ADE token. In the Intune admin center (intune.microsoft.com), go to Devices > Enrollment > Apple (see Get an Apple ADE token):

Select Enrollment program tokens and Add:

Then:
- Select I agree to grant Microsoft permission to send user and device information to Apple.
- Download the Intune public key certificate (in 2020: Download your public key).
- Select Create a token via Apple Business to open business.apple.com.

Sign in to Apple Business as an administrator:

In 2020 the next step was Settings > Device Management Settings > Add MDM Server:

Update (October 2026): in Apple Business, go to Devices > Management Services > Connect external device management, upload the public key (.pem) and select Download Service Token (see Link to an external device management service).
Name the MDM server, upload the public key (.pem) from Intune, select Save and download the token (.p7m):

Back in the Intune admin center, upload the token (.p7m), enter the Managed Apple Account you used to create it and select Next:

The connection to Apple Business is now active:

Note: like the Apple MDM push certificate, the ADE token is valid for one year. Renew it before it expires, and also when the account password changes or the admin who created it leaves.
Create an iOS/iPadOS enrollment policy
Intune admin center
Select your token and create the policy for ADE. In 2020 this was Profiles > Create profile > iOS/iPadOS:

Update (October 2026): enrollment profiles are now enrollment policies (Enrollment policies > Create policy > iOS/iPadOS). The older Profiles experience will be retired (see Set up ADE for iOS/iPadOS).
Enter a name and description. Under Management Settings, set:
- User affinity: Enroll with User Affinity
- Authentication method: Setup Assistant with modern authentication (recommended, iOS/iPadOS 13 and later)
- Locked enrollment: Yes
- Await final configuration: Yes (default for new policies)
In 2020 I used Company Portal as the authentication method, installed Company Portal with VPP and set Run Company Portal in Single App Mode until authentication to Yes:

Update (October 2026): Single App Mode is no longer supported and must be set to No, and the Sync with computers setting is gone. Microsoft recommends Setup Assistant with modern authentication: users sign in with Microsoft Entra ID and MFA in Setup Assistant, then sign in to Company Portal to finish the Entra registration (see Authentication methods for ADE). Await final configuration keeps the user at the end of Setup Assistant until the critical policies are installed. Intune ignores the Supervised setting on iOS/iPadOS 13 and later, because those devices are always supervised.
Under Setup Assistant, choose Hide or Show for each setup screen:

Note: the Passcode and Touch ID/Face ID screens don't work correctly on iOS 14.5 and later, and Microsoft recommends hiding them. My 2020 test still showed them.
When the policy is ready, select Set default policy (in 2020: Set default profile) so new devices added to Apple Business and synced to Intune get it automatically:

Create dynamic groups in Microsoft Entra ID
Microsoft Entra admin center
Dynamic groups (Microsoft Entra ID P1) are a good way to target policies and apps at iPhones and iPads. I suggest at least these three (see dynamic membership rules):
a) All corporate iOS/iPadOS devices
(device.managementType -eq "MDM") -and (device.deviceOwnership -eq "Company") -and ((device.deviceOSType -eq "iPad") -or (device.deviceOSType -eq "iPhone") -or (device.deviceOSType -eq "iPod"))b) All personal iOS/iPadOS devices
(device.managementType -eq "MDM") -and (device.deviceOwnership -ne "Company") -and ((device.deviceOSType -eq "iPad") -or (device.deviceOSType -eq "iPhone") -or (device.deviceOSType -eq "iPod"))c) Devices enrolled with your ADE policy, matched on the policy name:
(device.enrollmentProfileName -eq "ADE_Profile")
Tip: dynamic groups can delay the first policies and apps. Enrollment time grouping on the policy's Device group tab is a faster alternative.
Connect Intune to Apps and Books (VPP)
Intune admin center
In 2020 I downloaded the token in Apple Business Manager under Settings > Apps and Books > My Server Tokens:

Update (October 2026): in Apple Business, download the content token under Settings > Payments & Billing > Apps & Books (see Manage content tokens).
In the Intune admin center, go to Tenant administration > Connectors and tokens > Apple VPP Tokens > Create (see Manage Apple volume-purchased apps):

Upload the token file (.vpptoken) and enter the Managed Apple Account you used to download it:

Note: the content token is valid for one year. New token settings include the management type (MDM, or DDM for iOS 18 and later) and automatic app updates.
Back in Apple Business, open Apps and Books under Content, search for Intune Company Portal and get enough licences for all your users:

Note: free apps go through the same purchase process as paid apps.
Repeat it for every app you want to install silently, without Apple Accounts, for example Microsoft Edge and the Microsoft 365 apps. The purchased apps sync to Intune as iOS volume purchase program apps:

Note: Intune syncs the content token once a day. To sync now, go to Tenant administration > Connectors and tokens > Apple VPP Tokens, open the menu of your token and select Sync:

Assign the apps to your device group to install them silently on corporate iPhones and iPads:

Use Device licensing for these assignments (the default for new assignments today). Microsoft also recommends deploying Company Portal as a required VPP app with device licensing:

Add new and existing devices to Apple Business
Apple Business
There are two ways to add devices to Apple Business:
- Automatically, when you buy new devices from an Apple Authorised Reseller or carrier
- Manually, for devices bought elsewhere, with Apple Configurator for Mac or for iPhone
Update (October 2026): Apple Configurator can now also add Macs with Apple silicon or a T2 chip (macOS 12.0.1 and later), Apple TV (Ethernet models) and Apple Vision Pro, not only iPhones and iPads. For details, see Apple Business requirements.
You can set a default device management service for each device type (iPhone, iPad, Mac, Apple TV), so new devices are assigned to Intune automatically. In Apple Business this is Devices > Management Services > Default Device Assignment (see Assign, reassign or unassign devices):
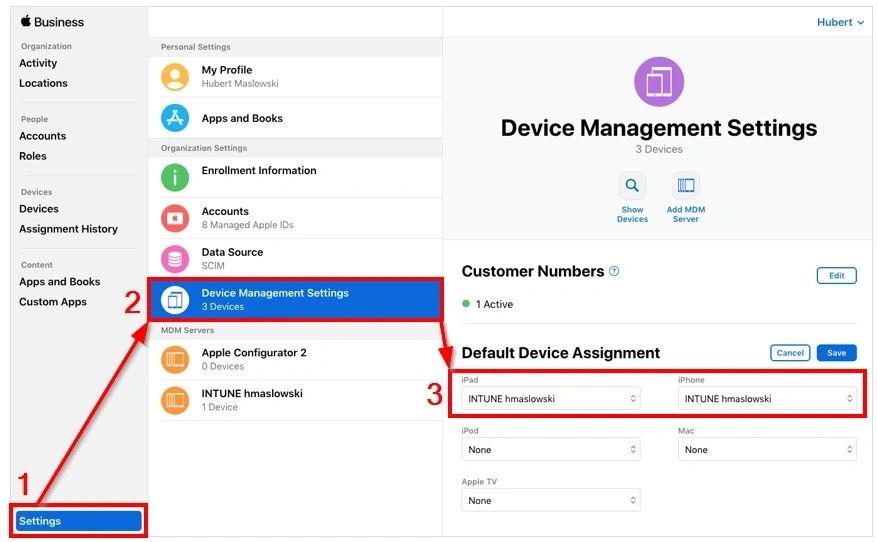
For my test I added an existing iPhone with iOS 13.6, not bought from a reseller, with Apple Configurator 2 on a Mac and a USB cable:

Then I assigned the iPhone to my Intune server manually. In 2020 this was Devices > (device) > Edit Device Management; in Apple Business it is now Devices > Inventory > (device) > Assign Device Management:

Devices assigned to your server sync to Intune and appear under Devices > Enrollment > Apple > Enrollment program tokens > (token) > Devices:

If the device appears in this list, it was added to ADE and assigned to Intune correctly.
Note: Intune runs a delta sync with Apple every 12 hours. You can start a manual sync at most every 15 minutes, and a full sync at most every 7 days (see Manage ADE tokens and devices).
The device shows Ready to enroll until the user unboxes it, connects to Wi-Fi or a mobile network and goes through Setup Assistant:

User Experience
A new iPhone goes through Setup Assistant and enrolls in Intune.
After Setup Assistant, the device is enrolled, shows as Corporate in the Intune admin center and joins the device groups that get its policies, profiles and apps. My 2020 test used Company Portal authentication with Single App Mode, so steps 4 to 7 look different with modern authentication.
1. On the Hello screen, press the Home button or swipe up, and select a language:

2. Select your country or region, and join a Wi-Fi network if there is no mobile data, to download the enrollment profile (Remote Management):

3. Setup Assistant shows only the screens left visible in the policy. In my case: Touch ID, Passcode and Location Services:


4. The message Guided Access app unavailable. Please contact your administrator. appeared because of Single App Mode: the device stayed locked until Company Portal was installed and opened:

5. Enter your password and select Sign in. With MFA, approve the sign-in, in my case in the Microsoft Authenticator app on another device:

6. On Set up company access, select Begin and then Continue:

7. On You're all set!, select Done:

8. The device is now enrolled and managed. The management profile is under Settings > General > VPN & Device Management (in iOS 13: Device Management):

9. The management profile on the device:

Note: for 30 days after a device is added with Apple Configurator, the user can still release it from management (Leave Remote Management). Devices bought from a reseller don't have this option.
10. The wallpaper changed, so the device features profile was installed. All required VPP apps install silently in the background, without asking the user to sign in with an Apple Account:

Intune admin center
In the Intune admin center (intune.microsoft.com):
The iPhone shows as Corporate:

It was added automatically to the dynamic group that matches the enrollment policy name:

It receives the profiles, policies and apps assigned to that group:
